الوسم: Data Breach

  • Data breach exposes files from India’s largest nuclear plant, Kudankulam

    Data breach exposes files from India’s largest nuclear plant, Kudankulam

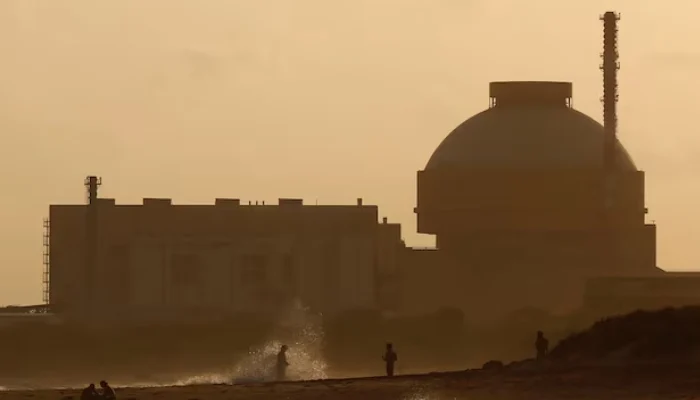
    World Leaks, a known ransomware group, has uploaded a vast collection of files on the dark web related to India’s largest nuclear power plant, including what appear to be blueprints and supplier information—claimed to originate from Reliance Group.

    Located in Tamil Nadu, the Kudankulam Nuclear Power Plant is the biggest of India’s seven nuclear facilities and a key element in Prime Minister Narendra Modi’s initiative to boost national nuclear energy production.

    Reliance Group, a contractor involved with the plant, informed Reuters that there was a “partial breach” of data stored on a third-party Indian data center provider Yotta’s server, and that authorities had been notified. The firm declined to specify what data was compromised.

    Nickolas Roth, senior director at the Nuclear Threat Initiative—an organization that advises governments on nuclear security—warned that this could pose a “serious” threat to the plant’s safety. The breach highlights the increasing frequency of cyberattacks in India, where many companies are poorly prepared for such threats.

    The leaked documents, reviewed by Reuters, span from 2016 to mid-2025, although their authenticity couldn’t be verified. They include blueprints, supplier listings, meeting records, inspection reports, equipment evaluations, and insurance policies. Of the 858,000 files associated with Reliance on the World Leaks website, about 19,000 appear to be the most sensitive.

    One Reliance subsidiary, Reliance Infrastructure, secured a 2018 contract to design and construct infrastructure for Units 3 and 4 of the plant, which are expected to operate by 2027 and will together provide 2,000 megawatts of power.

    The group behind the leak, World Leaks, has previously targeted companies like Nike and India’s Tata Group. It did not respond to Reuters questions about the Reliance breach. Typically, the group posts stolen corporate data online when companies refuse to pay ransom demands. Its website is accessible only via specialized browsers.

    In June, World Leaks claimed to have demanded $1.5 million to return Tata Group files containing confidential designs for Apple and Tesla, which they released after Tata apparently ignored the ransom.

    The Nuclear Power Corporation of India, responsible for operating the country’s nuclear plants, has engaged with Reliance about the breach. India’s main cybersecurity agency, CERT-In, is investigating, though officials declined to comment publicly. Reliance stated that suspicious activity was detected on May 29 on one of its servers and that action was taken immediately to stop the suspected ransomware attack. By the end of June, the company was informed of claims by external threat actors regarding a data breach. Yotta indicated it could not verify these claims but supported ongoing investigations.

    The posted documents do not seem to involve the reactors’ core systems, which are supplied by Russia’s Rosatom. They do include blueprints for ventilation, cooling systems, and the layout of a “common control room.” Some files appear to be vendor proposals, lists of approved suppliers, and records of inspections and meetings, including a 2024 joint review with photos of equipment.

    Additionally, one document suggests Reliance Infrastructure and the Nuclear Power Corporation held an insurance policy valued at $112 million, covering acts of terrorism in Units 3 or 4. Experts caution that if misused, these files could help adversaries map support systems, identify suppliers, or locate security vulnerabilities—potentially exposing how access to different parts of the plant is granted.

    India ranks third globally for data breaches, with 28.9 million accounts compromised last year, trailing only the U.S. and France, according to cybersecurity firm Surfshark. A report by the Data Security Council of India and Seqrite found that 73% of surveyed organizations were unsure if they had ever been attacked, and 57% lacked basic cyber hygiene practices.

    This isn’t the first time Kudankulam has faced cyber issues; in 2019, malware linked to North Korean hackers was discovered on its administrative network, though plant operations remained unaffected.

  • Iranian hackers hack FBI director’s email, leak photos and files

    Iranian hackers hack FBI director’s email, leak photos and files

    Iran-linked hackers have successfully infiltrated the personal email account of FBI Director Kash Patel, releasing numerous photographs and over 300 emails online, according to both the hackers and the FBI on Friday.

    The hacking group, Handala Hack Team, which claims ties to Iranian cyber intelligence, posted on their website that Patel “will now find his name among the list of successfully hacked victims.” They shared personal photos of Patel engaging in activities such as smoking cigars, riding in a vintage convertible, and making faces while posing with a large bottle of rum.

    The FBI has acknowledged that Patel’s emails were targeted. FBI spokesperson Ben Williamson stated, “We have taken all necessary measures to mitigate potential risks from this activity,” emphasizing that the compromised data was “historical in nature and does not involve any government information.”

    Handala, which positions itself as a pro-Palestinian vigilante hacking group, is widely considered by Western analysts to be a persona used by Iranian government cyber units. The group recently claimed responsibility for a March 11 breach of Michigan-based medical equipment and services provider Stryker, asserting they erased a large cache of corporate data.

    In addition to the photographs, the hackers released a sample of more than 300 emails, which appear to cover both personal and professional correspondence from 2010 to 2019. While Reuters could not independently authenticate the emails, the personal Gmail account linked to Handala matches previous leaks tied to Patel, according to dark web intelligence firm District 4 Labs. Google, which manages Gmail, has not yet responded to inquiries.

    Iran-linked hackers have increasingly brazenly publicized their cyber activities as tensions escalate between the U.S. and Iran. Besides the Stryker breach, Handala claimed on Thursday to have leaked the personal data of numerous Lockheed Martin employees based in the Middle East. Lockheed Martin responded by stating it has policies to address cyber threats.

    Cybersecurity experts suggest that these operations aim to destabilize and humiliate U.S. officials by exposing their vulnerabilities, a tactic Iran appears to be employing more openly as hostilities heighten. Such breaches of high-profile individuals’ personal emails are not unprecedented; past incidents include the hacking of Hillary Clinton’s campaign chairman John Podesta in 2016 and data leaks from then-CIA Director John Brennan’s AOL account in 2015.

    An intelligence assessment reviewed by Reuters on March 2 indicates that Iran and proxy groups may respond to recent U.S. military actions against Iran with low-level cyberattacks targeting American networks, illustrating a pattern of increased cyber retaliation.

    Harboring additional emails, Iran-linked hacking groups might have further damaging information in reserve. Last year, a group claiming to be “Robert” indicated intentions to release 100 gigabytes of data stolen from U.S. officials close to President Trump, including White House Chief of Staff Susie Wiles, though Reuters has been unable to verify this claim, and the group has been unresponsive in recent months.

  • Indian-American US cyber chief accused of leaking intel to ChatGPT

    Indian-American US cyber chief accused of leaking intel to ChatGPT

    The acting director of the Cybersecurity and Infrastructure Security Agency (CISA), Madhu Gottumukkala, is currently under investigation after reportedly uploading sensitive government contracting documents to the public version of ChatGPT. The documents, uploaded last summer, were not classified but carried the “For Official Use Only” label, indicating sensitive information not intended for public dissemination, according to Gulf News.

    The incident prompted internal cybersecurity alarms and a review by the Department of Homeland Security (DHS). A detailed report by Politico reveals that four DHS officials familiar with the case confirmed that the uploads triggered multiple automated security alerts designed to prevent unauthorized sharing of federal data.

    Gottumukkala, who has held the position of acting CISA director since May 2025, had obtained a temporary exemption from the agency’s Office of the Chief Information Officer to use ChatGPT while exploring artificial intelligence tools. At that time, most DHS employees were unable to access the platform due to security risks.

    In August 2025, cybersecurity sensors detected several uploads, including multiple alerts during the first week of the month. Senior DHS officials launched an internal investigation to determine if any security compromises resulted from the disclosures, though the results have not been publicly released.

    Marci McCarthy, CISA’s Director of Public Affairs, stated that Gottumukkala was granted permission to utilize ChatGPT under DHS-specific controls. She emphasized that the usage was intended to be short-term and restricted, and that the department normally blocks ChatGPT access unless explicitly approved. She added Gottumukkala last used ChatGPT in mid-July 2025 under a temporary, approved exception.

    Data input into the public ChatGPT version is shared with OpenAI and may be used to enhance responses for other users. OpenAI reports over 700 million active users. In contrast, DHS-approved internal AI systems, like the department’s DHSChat, are engineered to prevent data from leaving federal networks.

    Upon discovering the activity, Gottumukkala discussed the uploads with senior DHS officials, including acting General Counsel Joseph Mazzara and Chief Information Officer Antoine McCord, who reviewed potential security risks. He also consulted with CISA’s CIO Robert Costello and Chief Counsel Spencer Fisher to address the handling of “For Official Use Only” materials.

    The episode has intensified scrutiny of Gottumukkala’s leadership. Notably, at least six career staff members were placed on leave after he failed an unsanctioned counterintelligence polygraph exam, which he requested to take. During recent congressional testimony, Gottumukkala contested claims that he had failed the test, stating he did not “accept the premise” of such assertions.

    Currently, Gottumukkala is the highest-ranking political official at CISA, the federal agency responsible for protecting U.S. government networks and critical infrastructure from advanced cyber threats, including those originating from Russia and China.

  • UK Foreign Office Suffers Data Breach Attack

    UK Foreign Office Suffers Data Breach Attack

    A UK government official announced on Friday that an investigation is ongoing following a data breach at Britain’s Foreign Office in October. Trade Minister Chris Bryant confirmed that the Foreign, Commonwealth & Development Office (FCDO) was targeted, but downplayed reports linking Chinese hackers to the attack.

    This breach occurred after it was revealed in July that a Ministry of Defence employee accidentally exposed a document with the names and details of nearly 19,000 Afghans seeking relocation to the UK. Sensitive information of over 100 Britons, including intelligence operatives and special forces members, was also compromised.

    Bryant characterized the recent incident as “relatively low risk” and stated, “We’ve been investigating since October and have addressed the issue.” A report by The Sun indicated that a cybercriminal group called Storm-1849, accused of targeting critics of Beijing, might have been behind the breach.

    When asked if Chinese involvement could be ruled out, Bryant responded that he did not know. A government spokesperson emphasized that authorities are actively examining the incident and that they take the security of their systems and data very seriously.

    Cybercriminal groups have historically attacked UK institutions such as hospitals, postal services, luxury brands, and retailers.

  • Qantas Confirms Data Leak Affecting Millions of Customers

    Qantas Confirms Data Leak Affecting Millions of Customers

    Workers are seen near a Qantas Airways Boeing 737-800 plane parked at Adelaide Airport, Australia, August 22, 2018. — Reuters

    – Major cyberattack impacts global companies through Salesforce.
    – Sensitive customer information has been exposed, though no financial data was compromised.
    – Major tech and airline corporations targeted in the breach.

    A large-scale cyberattack has resulted in the theft of data from 5.7 million Qantas customers, which was subsequently leaked online as part of a broader security breach affecting numerous firms.

    Allegedly, prominent companies including Disney, Google, IKEA, Toyota, McDonald’s, and airlines such as Air France and KLM experienced data theft in an attack targeting Salesforce, a major software provider. The stolen information has been held hostage in ransom demands.

    Salesforce disclosed earlier this month that it was aware of recent extortion attempts by cybercriminals.

    Qantas announced in July that hackers infiltrated a third-party customer contact center, gaining access to a systems used by Salesforce. The breach exposed customer names, email addresses, phone numbers, and birthdays.

    Since then, no additional breaches have been reported, and the airline is working with Australian security agencies. The company stated that much of the leaked data comprised names, email addresses, and frequent flyer numbers. However, some information also included addresses, dates of birth, genders, meal preferences, and phone numbers.

    Qantas emphasized that credit card details, financial information, and passport data remained unaffected. The airline also secured a legal injunction from the Supreme Court of New South Wales to prevent the leaked data from being accessed or published.

    Cybersecurity expert Troy Hunt commented to AFP that such legal measures are unlikely to prevent the data’s further dissemination, calling the situation “ridiculous” and noting that security efforts do little to stop criminals outside of Australia.

    Google pointed AFP to a statement from August, confirming that one of its Salesforce servers was targeted, but did not confirm whether data was leaked. Melanie Lombardi, head of Google Cloud Security Communications, added that Google responded to the incident, assessed the impact, and notified potentially affected businesses.

    Analysts have linked the breach to hackers associated with the Scattered Lapsus$ Hunters, a cybercriminal alliance. According to research from Unit 42, the group claimed responsibility for attacking Salesforce tenants as part of a coordinated effort to steal and ransom data, with a deadline set for ransom payment on October 10.

    The hackers employed social engineering tactics, manipulating victims by impersonating company representatives to gain access—an approach last month warned against by the FBI. Experts say the attack was carried out using “the oldest tricks in the book” rather than sophisticated technical exploits.

    This incident, involving Australia’s largest airline, underscores increasing concerns about data security amid a string of high-profile cyberattacks in the country. Last year, Qantas apologized after a mobile app glitch exposed some passenger details, and in 2023, hacking of port systems handling nearly half of Australia’s freight trade brought operations to a halt.

  • Your Data May Be Stolen Again: 184 Million Logins Found

    Your Data May Be Stolen Again: 184 Million Logins Found

    A person using a laptop displaying a code.
    Sora Shimazaki / Pexels

    In a significant illustration of the ongoing risks found online, cybersecurity expert Jeremiah Fowler recently identified an enormous, unsecured database that revealed over 184 million login details from major platforms such as Microsoft, Apple, Facebook, Discord, Google, and PayPal. This data haul amounted to roughly 47.42 GB and was uncovered on an improperly configured cloud server. It is suspected that the data was gathered using infostealer malware—a type of malicious software engineered to extract sensitive information from compromised systems.

    A Global Breach with Major Consequences

    Fowler also discovered that the database included over 220 email addresses linked to government domains from at least 29 nations, including the United States, the United Kingdom, Australia, and Canada. This highlights the potential national security threats arising from such security breaches.

    An analysis of a 10,000-record subset revealed that the data encompassed plain text usernames and passwords, with some entries associated with financial terms such as “bank” and “wallet.” This suggests a higher risk of financial fraud. The presence of such sensitive data in an unprotected database raises serious concerns about identity theft, unauthorized access, and other cybercrimes. Additional images from the database provided by Jeremiah can be viewed on Hackread.com.

    The Mechanics of Infostealer Malware

    Infostealer malware typically infiltrates devices through phishing emails, malicious websites, or bundled within pirated software. Once installed, it can collect various data types, including login credentials, cookies, and autofill information, even details related to cryptocurrency wallets. This harvested data is then sent to command-and-control servers run by cybercriminals.

    The existence of this particular database indicates a systematic effort to gather and potentially misuse a massive amount of personal and institutional information. The lack of identifiable ownership or metadata complicates efforts to trace its origins or intended use, and hosting companies may be unaware they are harboring such databases.

    Immediate Responses and Suggested Steps

    After uncovering the database, Fowler quickly informed the hosting provider, World Host Group, which subsequently shut down the server. However, it remains unclear how long the data was exposed and whether unauthorized parties accessed it prior to its removal.

    Recommended Actions for Users

    • Change your passwords: Update your passwords for all online accounts, especially if you’ve reused passwords across multiple platforms.
    • Activate two-factor authentication (2FA): This usually requires a verification text sent to your phone or a secondary email.
    • Monitor your accounts: Keep an eye on your financial and other sensitive accounts for any unusual activity.
    • Utilize dependable security software: Ensure you have updated antivirus and malware protection from reputable sources.
    • Exercise caution with emails and downloads: Avoid clicking on suspicious links or downloading attachments from unknown senders.
  • 100 Million Affected In Largest U.S. Health Data Breach

    100 Million Affected In Largest U.S. Health Data Breach

    Previously, the largest health care data breach was recorded in 2015, impacting 78.8 million individuals. However, a new incident has significantly surpassed that figure.

    This latest cyberattack has reached an alarming scale, affecting an unprecedented 100 million people, and it has targeted UnitedHealth Group, the world’s largest health care company by revenue.

    The breach occurred in February 2024, following a ransomware attack that brought pharmacies across the nation to a standstill, according to initial reports from Reuters. The attack specifically targeted Change Healthcare, a subsidiary of UnitedHealth Group responsible for managing financial transactions for medical providers. Cybercriminals gained access to the Change Healthcare employee system due to insufficient multi-factor authentication for login credentials.

    A statement from the U.S. Senate Committee on Finance described the devastating consequences of the breach, which included unfilled prescriptions, unpaid doctors and hospitals, and insurance companies unable to reimburse medical providers. Senator Ron Wyden (D-Oregon) remarked, “The Change Healthcare hack is regarded by many as the most significant cybersecurity disruption in American health care history.”

    Approximately one-third of all U.S. citizens are somehow linked to Change Healthcare, which means a vast amount of personal information is at risk. The CEO of Change Healthcare noted that the compromised files included the personal health data of “a substantial proportion of people in America,” as reported by TechCrunch.

    The attack has been attributed to the BlackCat ransomware hacking group, a claim confirmed by Change Healthcare. This Russian-based group later boasted on the dark web about stealing health and patient information from millions of Americans.

    In a subsequent update, the U.S. Department of Health and Human Services revised the number of affected individuals in its data breach portal, revealing a staggering total of 100 million people. An industry publication even suggested that this figure might fluctuate, as covered by DailyMail. While this could indicate that the true number could be lower, it equally might rise.

    The scale of this breach makes the recent incident affecting 5.3 million records in Mexican health care systems seem trivial by comparison.

  • Comcast’s Xfinity Reports Data Breach Affecting 36 Million Customers

    Comcast’s Xfinity Reports Data Breach Affecting 36 Million Customers

    Comcast’s subsidiary, Xfinity, has found itself entangled in a significant data breach that has affected an estimated 36 million customers. The breach stemmed from a vulnerability discovered in Citrix software, termed “CitrixBleed,” which led to unauthorized access to sensitive customer information.

    The breach occurred between October 16 and 19, 2023, within Comcast’s internal systems. The intrusion came to light during a routine cybersecurity assessment on October 25, 2023, prompting swift actions from the company to address the issue and mitigate potential risks associated with the compromised data.

    The accessed information includes usernames and hashed passwords, with some customers potentially having additional data compromised, such as names, contact details, partial Social Security numbers, dates of birth, and secret questions and answers. Comcast initiated notifications to affected customers on December 18, 2023, through various communication channels, urging password resets and advising users to implement two-factor or multi-factor authentication as a security measure.

    As of the disclosure, Comcast asserted no knowledge of leaked customer data or direct attacks on its customers. However, a comprehensive investigation is underway to ascertain the full extent and ramifications of the breach.

    To safeguard against potential risks, Xfinity customers are advised to reset their passwords immediately and opt for enhanced authentication methods. Additionally, individuals using the same passwords across multiple services are encouraged to update their credentials across platforms and adopt unique passwords for each service to bolster security.

    The breach emphasizes the ongoing battle against cybersecurity threats, highlighting the importance of robust security measures and proactive responses to safeguard customer data in an increasingly digital landscape.