الوسم: Cybersecurity

  • US Turns to Private ‘Pirates’ in Bold Cybercrime Fight

    US Turns to Private ‘Pirates’ in Bold Cybercrime Fight

    A hooded man is depicted gripping a laptop computer, with cyber code projected onto him in this illustrative image — Reuters

    The U.S. is set to permit private companies to hack foreign cybercriminal groups, a move that’s sparking debate among experts. This initiative, seemingly without precedent, could either succeed or lead to chaos.

    On Wednesday, President Donald Trump issued a memorandum instructing the Justice and Homeland Security departments to authorize certain American companies to monitor and target international criminal organizations.

    The White House justified this stance by highlighting the substantial damage caused by ransomware, sextortion, and online fraud, which reportedly cost Americans over $20 billion in 2025.

    The directive allows private entities to take actions such as dismantling hackers’ servers or deploying spyware to infiltrate their systems. All operations will require prior government approval, and companies must post a security bond of at least $1 million.

    Activities that could result in death or injury are off-limits, as are any actions that would constitute “use of force” under international law.

    This approach resembles 18th-century privateering, where governments authorized private ships and sailors to raid enemy vessels. Ari Redbord, a former federal prosecutor now working at TRM Labs, explains, “The private sector controls the data, and the government holds the authority. This memorandum combines both.”

    Redbord sees a historical parallel in maritime privateering, noting, “Back then, once a ship left port, oversight was impossible. Today, technology allows continuous oversight from start to finish.”

    However, some experts express skepticism. University of Surrey cybersecurity professor Alan Woodward notes, “You can grant a commission, but obedience isn’t guaranteed. Historically, privateering was eventually considered problematic because it became more trouble than it was worth.”

    The memo marks a change in the White House’s stance. Previously, a senior U.S. official in March suggested the U.S. wasn’t interested in fighting cybercriminals with cybercriminals. Still, within five months, the administration reversed course.

    Columbia University researcher and former cybersecurity official Jason Healey sees some safeguards, stating, “They’re supporting this under the rule of law, so I don’t see it as reckless.” Yet, he cautions, “The current administration has systematically weakened agencies like the Office of the Director of National Intelligence that are supposed to oversee such actions.”

    Major U.S. tech companies already invest heavily in cybersecurity. The new program could extend their capabilities, enabling operations without judicial oversight, relying solely on government approval. Microsoft declined to comment, and Google did not respond to requests for comment.

    Redbord warns that companies engaging in government-sanctioned hacking could lose their neutrality and become targets themselves.

    The White House has 60 days to finalize the program’s specifics, though some details will remain classified. Its ultimate success or failure remains uncertain.

    Over time, Washington will need to weigh the program’s costs against potential benefits, such as the risk of misattributions, foreign prosecutions, and diplomatic issues, as Woodward points out.

    Cybercrimes continue to grow despite these efforts. Redbord emphasizes that, ultimately, unless victims recover their funds, most of the other concerns are secondary.

  • Your SIM Card Might Unknowingly Unlock Your Phone, Car, or EV Charger

    Your SIM Card Might Unknowingly Unlock Your Phone, Car, or EV Charger

    SIM cards have long been considered secure components within our smartphones and connected devices. However, recent research reveals that if a SIM card becomes malicious or compromised, it could serve as a powerful weapon for targeting the device it resides in.

    Researchers from the University of Birmingham, collaborating with cybersecurity firm Fuzzware, explored how malicious SIM cards can impact smartphones and Internet of Things (IoT) devices. They presented their findings at the 2026 USENIX WOOT Conference on Offensive Technologies in Baltimore.

    The core issue revolves around a technology called Proactive SIM, which enables a SIM card to send specific commands directly to a device’s modem. Among these commands are AT commands—an archaic command set initially developed to control modems decades ago.

    To evaluate the threat, the team developed a security testing toolkit called CATana, designed to simulate and analyze potential attacks. They tested 26 devices, including 18 smartphones and 8 IoT modules used in various systems like electric vehicle chargers, connected cars, and industrial machinery that communicate over cellular networks.

    The results were alarming: several devices accepted AT commands originating directly from the SIM card. This vulnerability could allow a malicious SIM to perform actions such as retrieving device identification information, sending messages, making calls, reactivating hidden debugging functions, disabling cellular connectivity, or even powering down the device. In more severe scenarios, attackers could execute commands on the device’s communication processor, potentially taking full control.

    Additionally, a hostile SIM could force devices to switch from secure 4G networks to the older, less secure 2G networks, increasing the risk of interception and attacks. The threat level is especially high for IoT devices like routers, vehicle systems, and industrial equipment, which are often designed with minimal interfaces to outside access. A SIM interface could provide an unexpected and dangerous pathway into these tightly secured systems.

    Beyond communications, the team discovered that on recent Android phones, a malicious SIM could prompt the device to open a malicious website without user interaction, even when the phone is locked.

    Various methods could enable an attacker to make a SIM malicious, including exploiting vulnerabilities in SIM software remotely, physically replacing a SIM card, compromising the mobile operator’s management systems, or tampering with SIMs during manufacturing or distribution.

    Partly rooted in older industry standards, many of the Proactive SIM features were initially designed under the assumption that SIM cards could be trusted. These outdated features may now pose unnecessary risks in today’s interconnected world.

    The researchers reported their findings to the GSMA and device manufacturers. Many companies have already released updates and improved device security configurations. While these steps enhance security across billions of SIM-enabled devices—from smartphones and vehicles to payment terminals and industrial controllers—they may only scratch the surface of the potential threats posed by malicious SIM cards.

    Their work highlights the need for continued vigilance and stronger safeguards, as the vulnerabilities uncovered suggest that the real scope of the risk could be much broader than currently understood.

  • Data breach exposes files from India’s largest nuclear plant, Kudankulam

    Data breach exposes files from India’s largest nuclear plant, Kudankulam

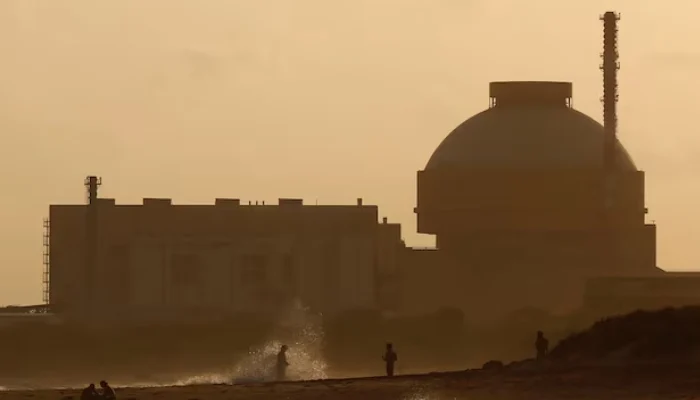
    World Leaks, a known ransomware group, has uploaded a vast collection of files on the dark web related to India’s largest nuclear power plant, including what appear to be blueprints and supplier information—claimed to originate from Reliance Group.

    Located in Tamil Nadu, the Kudankulam Nuclear Power Plant is the biggest of India’s seven nuclear facilities and a key element in Prime Minister Narendra Modi’s initiative to boost national nuclear energy production.

    Reliance Group, a contractor involved with the plant, informed Reuters that there was a “partial breach” of data stored on a third-party Indian data center provider Yotta’s server, and that authorities had been notified. The firm declined to specify what data was compromised.

    Nickolas Roth, senior director at the Nuclear Threat Initiative—an organization that advises governments on nuclear security—warned that this could pose a “serious” threat to the plant’s safety. The breach highlights the increasing frequency of cyberattacks in India, where many companies are poorly prepared for such threats.

    The leaked documents, reviewed by Reuters, span from 2016 to mid-2025, although their authenticity couldn’t be verified. They include blueprints, supplier listings, meeting records, inspection reports, equipment evaluations, and insurance policies. Of the 858,000 files associated with Reliance on the World Leaks website, about 19,000 appear to be the most sensitive.

    One Reliance subsidiary, Reliance Infrastructure, secured a 2018 contract to design and construct infrastructure for Units 3 and 4 of the plant, which are expected to operate by 2027 and will together provide 2,000 megawatts of power.

    The group behind the leak, World Leaks, has previously targeted companies like Nike and India’s Tata Group. It did not respond to Reuters questions about the Reliance breach. Typically, the group posts stolen corporate data online when companies refuse to pay ransom demands. Its website is accessible only via specialized browsers.

    In June, World Leaks claimed to have demanded $1.5 million to return Tata Group files containing confidential designs for Apple and Tesla, which they released after Tata apparently ignored the ransom.

    The Nuclear Power Corporation of India, responsible for operating the country’s nuclear plants, has engaged with Reliance about the breach. India’s main cybersecurity agency, CERT-In, is investigating, though officials declined to comment publicly. Reliance stated that suspicious activity was detected on May 29 on one of its servers and that action was taken immediately to stop the suspected ransomware attack. By the end of June, the company was informed of claims by external threat actors regarding a data breach. Yotta indicated it could not verify these claims but supported ongoing investigations.

    The posted documents do not seem to involve the reactors’ core systems, which are supplied by Russia’s Rosatom. They do include blueprints for ventilation, cooling systems, and the layout of a “common control room.” Some files appear to be vendor proposals, lists of approved suppliers, and records of inspections and meetings, including a 2024 joint review with photos of equipment.

    Additionally, one document suggests Reliance Infrastructure and the Nuclear Power Corporation held an insurance policy valued at $112 million, covering acts of terrorism in Units 3 or 4. Experts caution that if misused, these files could help adversaries map support systems, identify suppliers, or locate security vulnerabilities—potentially exposing how access to different parts of the plant is granted.

    India ranks third globally for data breaches, with 28.9 million accounts compromised last year, trailing only the U.S. and France, according to cybersecurity firm Surfshark. A report by the Data Security Council of India and Seqrite found that 73% of surveyed organizations were unsure if they had ever been attacked, and 57% lacked basic cyber hygiene practices.

    This isn’t the first time Kudankulam has faced cyber issues; in 2019, malware linked to North Korean hackers was discovered on its administrative network, though plant operations remained unaffected.

  • Indian News Channels ‘Hacked’ During President’s Address

    Indian News Channels ‘Hacked’ During President’s Address

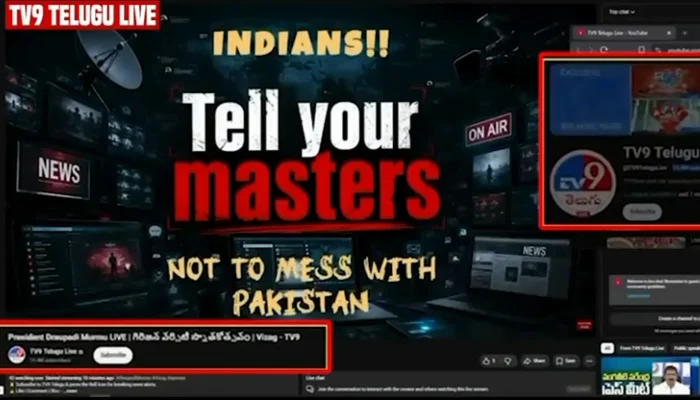
    Unidentified hackers compromised the broadcasting systems of two Indian news channels during the Indian president’s speech, allegedly inserting Pakistan’s national anthem and displaying a warning message, according to reports on Wednesday.

    It was reported that both TV9 Telugu and Freedom TV Kannada experienced disruptions while live. The hackers reportedly accessed the channels’ transmission feeds during the president’s address. During the incident on TV9 Telugu, Pakistan’s national anthem was broadcast, and a warning appeared, cautioning viewers against provoking Pakistan.

    Following the incident, rumors and varied explanations circulated regarding the broadcast interruption. TV9 Telugu has over 14 million followers on social media, and Freedom TV Kannada boasts more than one million followers.

    Industry experts commented that this event revealed security vulnerabilities within India’s cybersecurity infrastructure and highlighted weaknesses in the country’s IT systems.

  • Your Smart Home Devices Might Be Part Of A Cybercrime Network

    Your Smart Home Devices Might Be Part Of A Cybercrime Network

    Smart home gadgets and devices are now a common feature in many contemporary households. Security cameras monitor front doors, streaming devices power up TVs, and connected appliances continuously share data over the internet. While many people are concerned about corporations gathering too much personal information, a rising cybersecurity threat indicates that consumers might face an even larger problem.

    Security experts are warning that some internet-connected devices may harbor hidden software backdoors or critical security vulnerabilities that could allow outside parties to access home networks. In certain cases, these devices can covertly transform a household’s internet connection into a tool for cybercriminals without the homeowner’s awareness.

    How compromised smart devices are being exploited

    Many of these compromised devices are connected to what are known as residential proxy networks. These services reroute internet traffic through actual household connections, making online activities appear as if they originate from an ordinary home rather than a data center, VPN, or suspicious network.

    While residential proxies serve legitimate purposes, such as testing websites or ads from different regions, problems arise when consumers unknowingly become part of these networks.

    According to a recent Wall Street Journal investigation, some digital picture frames and streaming media players appeared to contain software that automatically connected them to residential proxy services. Experts interviewed in the report believe certain manufacturers might be paid to embed this software before the devices reach consumers.

    Once connected, these devices can silently transmit internet traffic for third parties. Monitoring of several test units revealed activity linked to gambling sites, cryptocurrency platforms, adult content, and online account access attempts.

    Why this presents a concern for users

    Having strangers route traffic through your home internet creates significant privacy and security risks. Malicious actors using a household’s connection can make it look like the house itself is involved in illegal activity. Security experts associate these networks with fraud, ticket scalping, ad fraud, and unauthorized account usage.

    The risk escalates further when cybercriminals gain direct control over vulnerable devices. Evidence shows hackers repeatedly attempt to access internet-connected gadgets, sometimes turning them into parts of massive botnets used to orchestrate distributed denial-of-service attacks (DDoS). Industry estimates suggest tens of millions, possibly hundreds of millions, of devices worldwide could be at risk.

    Steps you can take to safeguard yourself

    Individuals can lower their risk by purchasing devices from trusted manufacturers, regularly updating device firmware, and steering clear of suspiciously cheap products from unknown brands. Experts also advise avoiding unverified apps and sideloaded software, as these can introduce malware into your smart devices. Placing smart home devices on a separate guest network can help contain potential damage if a device becomes compromised and prevent hackers from accessing your phones, laptops, or other sensitive gadgets on the same network.

  • Pentagon: US Military Faces Location Data Targeting Threats

    Pentagon: US Military Faces Location Data Targeting Threats

    U.S. service members deployed to combat zones have been targeted through the use of commercially available location data, highlighting how the global surveillance economy influences modern warfare. According to a letter shared with Reuters by Oregon Senator Ron Wyden, Central Command indicated it had “received multiple threat reports concerning enemy exploitation of commercial location data to locate or monitor U.S. personnel in the area.” The message, dated April 14, did not reveal further details, but Central Command’s jurisdiction includes the Persian Gulf, where U.S. forces are engaged with Iran over the Strait of Hormuz.

    This marks the first official acknowledgment that U.S. troops in active conflict zones have been targeted using civilian location data, lawmakers noted in a letter to the Pentagon. “Commercial location data can reveal where U.S. troops gather and their daily routines, which adversaries can exploit to launch missile, drone, or roadside bomb attacks, as well as for counterintelligence,” the letter warned. Wyden emphasized that it’s time to treat the adtech industry as a national security concern.

    The Pentagon did not respond to requests for comment, and lawmakers reported difficulty obtaining additional information from military officials regarding the targeting incidents.

    Location data, predominantly used in digital advertising—a lucrative revenue source for many technology firms—is collected from smartphones and devices through apps or services, then sold to brokers who repackage and sell it through layered networks. While concerns over privacy and the sale of movement data have been publicly discussed for years, recent revelations have raised alarm over potential national security threats.

    As early as 2016, a U.S. defense contractor used commercial location data to track special operations forces from U.S. bases to a sensitive staging area in Syria, a fact first reported by the Wall Street Journal. More recently, Wired and two German news outlets analyzed billions of geolocation points collected by data brokers to expose detailed movements around 11 U.S. military and intelligence sites in Germany.

    Representatives from the Interactive Advertising Bureau and the Association of National Advertisers did not respond to requests for comment. The lawmakers’ letter pointed out that, given what the military knows about the commercial location data trade, there was a failure to act swiftly to safeguard personnel—such as disabling advertising IDs on military-issued devices, turning off location sharing on smartphones, or steering users away from browsers like Chrome toward more privacy-minded options.

    North Carolina Republican and former U.S. Army Special Forces officer Pat Harrigan co-signed the letter, describing Chrome as “built to collect and share user data,” and warning that each day it remains on government devices is “another day we’re giving adversaries a weapon against our troops.”

    In response, Google stated that Chrome offers “industry-leading security” and has long supported efforts for stronger privacy rules and protections against data brokers.

  • Hormuz Digital Strait: Middle East Conflict’s Impact on Subsea Cables

    Iran issued a warning last week regarding the vulnerability of submarine cables in the Strait of Hormuz, emphasizing their importance to the region’s digital economy and raising alarms about potential targeted attacks on critical infrastructure.

    This strategic waterway, already recognized as a major choke point for global oil shipments, is also crucial for digital connectivity. Multiple fiber-optic cables run beneath the seabed of the strait, linking countries from India and Southeast Asia to Europe through Gulf states and Egypt.

    Why are undersea cables vital?

    Subsea cables, which are fiber-optic or electrical lines laid on the ocean floor, facilitate the transmission of data and electricity. They handle approximately 99% of global internet traffic, as stated by the International Telecommunication Union (ITU), a UN agency dedicated to digital technologies.

    Beyond internet data, these cables support international telecommunications and power transfers, underpinning cloud services and online communications worldwide.

    “Any damage to these cables can lead to slower internet speeds or outages, disrupt e-commerce, delay financial transactions, resulting in considerable economic impacts,” explained Masha Kotkin, a geopolitical and energy analyst.

    Gulf nations like the UAE and Saudi Arabia have invested heavily in artificial intelligence and digital infrastructure, aiming to diversify their economies beyond oil. Their national AI companies depend on these underwater cables to transfer vast amounts of data at rapid speeds.

    Key cables passing through the Strait include the Asia-Africa-Europe 1 (AAE-1), linking Southeast Asia to Europe via Egypt with GTF landing points in the UAE, Oman, Qatar, and Saudi Arabia; the FALCON network connecting India and Sri Lanka to Gulf countries, Sudan, and Egypt; and the Gulf Bridge International Cable System, which connects all Gulf countries, including Iran.

    Ongoing projects include a system spearheaded by Qatar’s Ooredoo.

    What are the main risks?

    Despite the rapid expansion of submarine cable networks from 2014 to 2025, the annual fault rate remains steady at about 150 to 200 incidents, according to the ICPC. While state-backed sabotage is a concern, most faults—70 to 80%—are accidental, caused by fishing activities or ships dropping anchors.

    Other hazards include undersea currents, earthquakes, submarine volcanoes, and typhoons. Industry experts like Alan Mauldin say companies mitigate these risks by burying cables, reinforcing them with armor, and choosing safer routes.

    The ongoing conflict between the US, Israel, and Iran, now nearing two months, has led to significant disruptions across regional infrastructure and the global energy supply, including attacks on data centers in Bahrain and the UAE. Fortunately, subsea cables have remained unscathed so far.

    However, there’s an added danger from vessels inadvertently damaging cables during military operations by dragging anchors. As Masha Kotkin notes, “With active hostilities continuing, the risk of unintentional damage increases, especially the longer the conflict persists.” A previous incident in 2024 involved a vessel attacked by Iran-backed Houthis that drifted in the Red Sea and severed cables with its anchor.

    The extent of connectivity disruption for Gulf countries will largely depend on how heavily individual networks rely on these cables and whether alternative routes exist.

    Challenges in repair

    Restoring damaged cables, especially in conflict zones, presents numerous challenges. While physically repairing the cables isn’t overly complicated, factors such as security concerns, the risk of fighting, mines, or the presence of wreckage can complicate access. Obtaining permits to enter territorial waters can also cause delays; Mauldin explains this process can sometimes be time-consuming and problematic.

    Post-conflict, companies will need to re-examine the seabed to update safe cable routes and steer clear of wreckage or other hazards left behind during hostilities.

    What if subsea cables are compromised?

    While land-based links ensure that total internet shutdowns are improbable, experts agree that satellite systems cannot fully substitute for undersea cables, primarily because they lack the capacity to handle heavy data loads and are more costly.

    Mauldin emphasizes, “Switching completely to satellites isn’t a practical option,” noting that satellites work better for mobile or moving platforms like airplanes and ships.

    Low-Earth orbit networks such as Starlink currently serve as niche solutions, limited in scalability to serve millions of users, according to Kotkin.

  • Iranian hackers hack FBI director’s email, leak photos and files

    Iranian hackers hack FBI director’s email, leak photos and files

    Iran-linked hackers have successfully infiltrated the personal email account of FBI Director Kash Patel, releasing numerous photographs and over 300 emails online, according to both the hackers and the FBI on Friday.

    The hacking group, Handala Hack Team, which claims ties to Iranian cyber intelligence, posted on their website that Patel “will now find his name among the list of successfully hacked victims.” They shared personal photos of Patel engaging in activities such as smoking cigars, riding in a vintage convertible, and making faces while posing with a large bottle of rum.

    The FBI has acknowledged that Patel’s emails were targeted. FBI spokesperson Ben Williamson stated, “We have taken all necessary measures to mitigate potential risks from this activity,” emphasizing that the compromised data was “historical in nature and does not involve any government information.”

    Handala, which positions itself as a pro-Palestinian vigilante hacking group, is widely considered by Western analysts to be a persona used by Iranian government cyber units. The group recently claimed responsibility for a March 11 breach of Michigan-based medical equipment and services provider Stryker, asserting they erased a large cache of corporate data.

    In addition to the photographs, the hackers released a sample of more than 300 emails, which appear to cover both personal and professional correspondence from 2010 to 2019. While Reuters could not independently authenticate the emails, the personal Gmail account linked to Handala matches previous leaks tied to Patel, according to dark web intelligence firm District 4 Labs. Google, which manages Gmail, has not yet responded to inquiries.

    Iran-linked hackers have increasingly brazenly publicized their cyber activities as tensions escalate between the U.S. and Iran. Besides the Stryker breach, Handala claimed on Thursday to have leaked the personal data of numerous Lockheed Martin employees based in the Middle East. Lockheed Martin responded by stating it has policies to address cyber threats.

    Cybersecurity experts suggest that these operations aim to destabilize and humiliate U.S. officials by exposing their vulnerabilities, a tactic Iran appears to be employing more openly as hostilities heighten. Such breaches of high-profile individuals’ personal emails are not unprecedented; past incidents include the hacking of Hillary Clinton’s campaign chairman John Podesta in 2016 and data leaks from then-CIA Director John Brennan’s AOL account in 2015.

    An intelligence assessment reviewed by Reuters on March 2 indicates that Iran and proxy groups may respond to recent U.S. military actions against Iran with low-level cyberattacks targeting American networks, illustrating a pattern of increased cyber retaliation.

    Harboring additional emails, Iran-linked hacking groups might have further damaging information in reserve. Last year, a group claiming to be “Robert” indicated intentions to release 100 gigabytes of data stolen from U.S. officials close to President Trump, including White House Chief of Staff Susie Wiles, though Reuters has been unable to verify this claim, and the group has been unresponsive in recent months.

  • UAE disrupts planned cyber strikes on critical digital sectors

    UAE disrupts planned cyber strikes on critical digital sectors

    The UAE has successfully prevented organized cyber attacks aimed at its digital infrastructure and critical sectors, according to the state news agency on Saturday. These assaults involved attempts to breach networks, distribute ransomware, and carry out coordinated phishing operations targeting key national platforms. Authorities also revealed that artificial intelligence tools had been utilized to create offensive cyber capabilities.

    The Cybersecurity Council emphasized from the outset that safeguarding individuals, protecting personal data, and maintaining essential services are paramount. The country’s cybersecurity and cyber defense systems continue to operate effectively, ensuring high levels of protection and resilience.

    Recent security incidents highlighted ongoing efforts by malicious actors to infiltrate networks and compromise sensitive systems. Citizens are encouraged to stay vigilant and report any suspicious cyber activities through official channels to help maintain the nation’s digital safety and ensure uninterrupted government and business operations.

  • Indian-American US cyber chief accused of leaking intel to ChatGPT

    Indian-American US cyber chief accused of leaking intel to ChatGPT

    The acting director of the Cybersecurity and Infrastructure Security Agency (CISA), Madhu Gottumukkala, is currently under investigation after reportedly uploading sensitive government contracting documents to the public version of ChatGPT. The documents, uploaded last summer, were not classified but carried the “For Official Use Only” label, indicating sensitive information not intended for public dissemination, according to Gulf News.

    The incident prompted internal cybersecurity alarms and a review by the Department of Homeland Security (DHS). A detailed report by Politico reveals that four DHS officials familiar with the case confirmed that the uploads triggered multiple automated security alerts designed to prevent unauthorized sharing of federal data.

    Gottumukkala, who has held the position of acting CISA director since May 2025, had obtained a temporary exemption from the agency’s Office of the Chief Information Officer to use ChatGPT while exploring artificial intelligence tools. At that time, most DHS employees were unable to access the platform due to security risks.

    In August 2025, cybersecurity sensors detected several uploads, including multiple alerts during the first week of the month. Senior DHS officials launched an internal investigation to determine if any security compromises resulted from the disclosures, though the results have not been publicly released.

    Marci McCarthy, CISA’s Director of Public Affairs, stated that Gottumukkala was granted permission to utilize ChatGPT under DHS-specific controls. She emphasized that the usage was intended to be short-term and restricted, and that the department normally blocks ChatGPT access unless explicitly approved. She added Gottumukkala last used ChatGPT in mid-July 2025 under a temporary, approved exception.

    Data input into the public ChatGPT version is shared with OpenAI and may be used to enhance responses for other users. OpenAI reports over 700 million active users. In contrast, DHS-approved internal AI systems, like the department’s DHSChat, are engineered to prevent data from leaving federal networks.

    Upon discovering the activity, Gottumukkala discussed the uploads with senior DHS officials, including acting General Counsel Joseph Mazzara and Chief Information Officer Antoine McCord, who reviewed potential security risks. He also consulted with CISA’s CIO Robert Costello and Chief Counsel Spencer Fisher to address the handling of “For Official Use Only” materials.

    The episode has intensified scrutiny of Gottumukkala’s leadership. Notably, at least six career staff members were placed on leave after he failed an unsanctioned counterintelligence polygraph exam, which he requested to take. During recent congressional testimony, Gottumukkala contested claims that he had failed the test, stating he did not “accept the premise” of such assertions.

    Currently, Gottumukkala is the highest-ranking political official at CISA, the federal agency responsible for protecting U.S. government networks and critical infrastructure from advanced cyber threats, including those originating from Russia and China.

  • UK Foreign Office Suffers Data Breach Attack

    UK Foreign Office Suffers Data Breach Attack

    A UK government official announced on Friday that an investigation is ongoing following a data breach at Britain’s Foreign Office in October. Trade Minister Chris Bryant confirmed that the Foreign, Commonwealth & Development Office (FCDO) was targeted, but downplayed reports linking Chinese hackers to the attack.

    This breach occurred after it was revealed in July that a Ministry of Defence employee accidentally exposed a document with the names and details of nearly 19,000 Afghans seeking relocation to the UK. Sensitive information of over 100 Britons, including intelligence operatives and special forces members, was also compromised.

    Bryant characterized the recent incident as “relatively low risk” and stated, “We’ve been investigating since October and have addressed the issue.” A report by The Sun indicated that a cybercriminal group called Storm-1849, accused of targeting critics of Beijing, might have been behind the breach.

    When asked if Chinese involvement could be ruled out, Bryant responded that he did not know. A government spokesperson emphasized that authorities are actively examining the incident and that they take the security of their systems and data very seriously.

    Cybercriminal groups have historically attacked UK institutions such as hospitals, postal services, luxury brands, and retailers.

  • Qantas Confirms Data Leak Affecting Millions of Customers

    Qantas Confirms Data Leak Affecting Millions of Customers

    Workers are seen near a Qantas Airways Boeing 737-800 plane parked at Adelaide Airport, Australia, August 22, 2018. — Reuters

    – Major cyberattack impacts global companies through Salesforce.
    – Sensitive customer information has been exposed, though no financial data was compromised.
    – Major tech and airline corporations targeted in the breach.

    A large-scale cyberattack has resulted in the theft of data from 5.7 million Qantas customers, which was subsequently leaked online as part of a broader security breach affecting numerous firms.

    Allegedly, prominent companies including Disney, Google, IKEA, Toyota, McDonald’s, and airlines such as Air France and KLM experienced data theft in an attack targeting Salesforce, a major software provider. The stolen information has been held hostage in ransom demands.

    Salesforce disclosed earlier this month that it was aware of recent extortion attempts by cybercriminals.

    Qantas announced in July that hackers infiltrated a third-party customer contact center, gaining access to a systems used by Salesforce. The breach exposed customer names, email addresses, phone numbers, and birthdays.

    Since then, no additional breaches have been reported, and the airline is working with Australian security agencies. The company stated that much of the leaked data comprised names, email addresses, and frequent flyer numbers. However, some information also included addresses, dates of birth, genders, meal preferences, and phone numbers.

    Qantas emphasized that credit card details, financial information, and passport data remained unaffected. The airline also secured a legal injunction from the Supreme Court of New South Wales to prevent the leaked data from being accessed or published.

    Cybersecurity expert Troy Hunt commented to AFP that such legal measures are unlikely to prevent the data’s further dissemination, calling the situation “ridiculous” and noting that security efforts do little to stop criminals outside of Australia.

    Google pointed AFP to a statement from August, confirming that one of its Salesforce servers was targeted, but did not confirm whether data was leaked. Melanie Lombardi, head of Google Cloud Security Communications, added that Google responded to the incident, assessed the impact, and notified potentially affected businesses.

    Analysts have linked the breach to hackers associated with the Scattered Lapsus$ Hunters, a cybercriminal alliance. According to research from Unit 42, the group claimed responsibility for attacking Salesforce tenants as part of a coordinated effort to steal and ransom data, with a deadline set for ransom payment on October 10.

    The hackers employed social engineering tactics, manipulating victims by impersonating company representatives to gain access—an approach last month warned against by the FBI. Experts say the attack was carried out using “the oldest tricks in the book” rather than sophisticated technical exploits.

    This incident, involving Australia’s largest airline, underscores increasing concerns about data security amid a string of high-profile cyberattacks in the country. Last year, Qantas apologized after a mobile app glitch exposed some passenger details, and in 2023, hacking of port systems handling nearly half of Australia’s freight trade brought operations to a halt.

  • How Does Hacking Work in Upload Labs: Completing and Solving Roles

    How Does Hacking Work in Upload Labs: Completing and Solving Roles

    Once you have the basics of Upload Labs down, the next step is to learn more advanced features, starting with hacking. Like many of the late-game options, hacking takes some time to get started, but once you do, it produces valuable resources that give you big advantages.

    If you’re confused about how hacking and breaching work in Upload Labs or what your goals are, this guide explains it all clearly.

    Hacking and Breaching

    After unlocking hacking from the research screen, you can place the Hack Interface node. This is the starting point for all your hacking activities. The node’s level determines how much Hack Power it generates, which can be used in attack nodes to cause damage. These attacks are then directed at targets to break into them.

    Hack Power can be divided among multiple attacks and targets. You decide whether to hit several targets at once for smaller amounts or focus everything on one. When you unlock Hack Skills, you can also modify attacks by routing damage through Skill nodes before reaching the target.

    Your initial attack is called Launch Payload, which does damage based on how much Hack Power it gets. Later, you can unlock Infect, which causes more damage over time if left attacking longer. Both can be upgraded and customized with Skills.

    Breaching Targets

    At first, you can only hack one target: Anonymous. As you progress and unlock more research, you’ll be able to hack into corporations, governments, and banks. These different targets work similarly, but they offer different rewards.

    When you send attack damage to a target, a timer at the bottom of its node starts counting down. Usually, it’s five seconds, but you can buy the Sneak Attack upgrade to increase it. To successfully breach a target, you need to deal enough damage before the timer hits zero.

    If the target has any Firewall remaining, your attack damage will first remove it. After the Firewall is gone, damage fills a breach meter. The hack is successful when this meter is full; the node flashes green, and the rewards are either stored or sent to the output node if available. If the timer ends first, the node flashes red, and you get no rewards for that attempt. There are no penalties, just no gains.

    Threat Level

    The Threat Level of a target shows how tough it is to hack. It affects the Firewall and breach meter strength. All targets start at Threat Level 1. You unlock higher levels by successfully breaching the level below at least once. Once unlocked, you can freely raise or lower the Threat Level up to the highest one you’ve unlocked.

    It’s generally better to hack targets with higher Threat Levels because they give better rewards. So aim to handle the highest Threat Level you’re comfortable with.

    Breach Targets and Rewards

    | Target | Breach Reward | Sent To | Used For |
    |————–|———————|——————————|——————————————————————————————————–|
    | Anonymous | Hack Experience | Hack Terminal | Increases Hack Terminal level and earns points for hacking upgrades. |
    | Corporation | Corporate Data | Collector/Auto Collector | Spent on upgrades that lower costs and increase earnings. |
    | Government | Government Intel | Collector/Auto Collector | Used to buy upgrades that boost research. |
    | Bank | Tokens | Automatically collected | Unique to each bank; spawns randomly, with only one chance to breach when they appear. |

    Trojans

    As you advance, you’ll gain the ability to produce Trojans at your Hack Terminal. These are generated automatically based on the Terminal’s level and do not require Hack Power—they’re a separate resource. Trojans can be sent to an Inject Trojan node, where they get added to files placed in that node. This process doesn’t change the file size or value.

    Placing a Trojan into a file that has been scanned for viruses will remove its Scanned status. When you sell a file with an attached Trojan, it produces a new resource called Infected Computers. These can be sent to a Drain Node, which connects to a Network, Processor, or GPU to boost its performance. The more Infected Computers connected, the higher the performance boost you’ll receive.

  • Cyberattack Hits European Airports, Disrupting Heathrow and Brussels

    Cyberattack Hits European Airports, Disrupting Heathrow and Brussels

    A cyberattack targeting a provider of check-in and boarding system services caused significant disruptions at several major European airports, including London’s Heathrow, Brussels, and Berlin, resulting in delays and cancellations on Saturday. Collins Aerospace, which supplies check-in and boarding technology to numerous airlines worldwide, is experiencing a technical glitch that may lead to delays for travelers departing from affected airports, according to London Heathrow. The parent company, RTX, did not respond immediately outside U.S. business hours.

    The attack has disabled automated systems, forcing airports to rely on manual check-in and boarding procedures. Brussels Airport issued a statement on its website indicating the situation has considerably impacted flight schedules, leading to delays and cancellations. The airport is actively working to resolve the issue as quickly as possible.

    Travelers scheduled to fly on Saturday were advised by the affected airports to verify their flight status with airlines before arriving at the airport. Berlin Airport also issued a notice on its website, stating, “Due to a technical problem with a system provider operating across Europe, check-in times are longer than usual. We are working on a quick solution.” However, Frankfurt, Germany’s largest airport, confirmed it was not affected, nor was Zurich Airport’s operations impacted.

    The disruption has led most other airports to issue advisories urging passengers to check their flight statuses prior to travel, emphasizing ongoing efforts to restore normal operations amid the cyberattack.

  • Cyberattacks Shock UK Retailers: M&S Hits £700M Loss in Days

    Cyberattacks Shock UK Retailers: M&S Hits £700M Loss in Days

    Sure! Here’s a rewritten version of the content in American English, maintaining its essence while making it unique and plagiarism-free:

    —

    A contactless payment card reader at an M&S Food Hall in London, UK on April 30, 2025. Reuters

    LONDON: Several major retailers in the UK have faced significant setbacks due to recent cyberattacks, with Marks & Spencer (M&S) suffering a loss of £700 million in market value within a week and still unable to fulfill online orders.

    Entering their second week of disrupted online orders, M&S experienced a major cyber incident last week, while the Co-op Group disclosed that hackers had compromised customer data.

    Since the hacking incident was disclosed, M&S has seen a £700 million ($930 million) drop in its stock market valuation. The recent troubles faced by the Co-op and Harrods, a London department store, prompted the UK’s National Cyber Security Centre (NCSC) to label these incidents a “wake-up call.”

    In recent years, British companies, public institutions, and organizations have been under a barrage of cyberattacks that have cost them millions and often led to months of operational disruptions.

    M&S, a well-established name in British retail for 141 years, halted clothing and home goods orders via its website and app starting April 25, following issues with contactless payment and click-and-collect services over the Easter bank holiday weekend.

    The Co-op initially announced a cyberattack on Wednesday but revealed on Friday that sensitive information related to many current and former members—such as names, contact information, and dates of birth—had been compromised.

    Ciaran Martin, the former CEO of the NCSC, told Reuters that currently, there’s no indication that the attacks on M&S, the Co-op, and Harrods are interconnected, suggesting that the latter two incidents might have been uncovered due to increased alertness following M&S’s breach.

    “If this can happen to M&S, it could happen to anyone,” he remarked, emphasizing that recovery from such a significant attack often takes a considerable amount of time.

    On Friday, M&S CEO Stuart Machin issued another apology to customers but did not provide a timeline for restoring online ordering.

    “We are working tirelessly to manage the current cyber incident and aim to return to normal operations for you as swiftly as possible,” he communicated in an email to M&S customers.

    With M&S operating approximately 1,000 stores in the UK and generating about one-third of its clothing and home sales online, analysts predict a temporary decline in profits is unavoidable.

    While M&S has refrained from disclosing the financial impact, it continues to grow as they miss sales opportunities for new seasonal collections amid a record-breaking hot May in the UK.

    Last year, commuters faced nearly three months of account lockouts following a cyberattack on London’s transport authority, TfL. Another assault on a blood testing processing company in London also disrupted services for over three months.

    Some food items have been affected in specific M&S locations, and broader disruptions appear to be impacting the company, which has removed job postings from its website.

    M&S shares closed down by 1%, bringing their losses since Easter to about 9%.

    ‘Increasingly Sophisticated’ Attacks

    Helen Dickinson, CEO of the British Retail Consortium, noted that cyberattacks are becoming “more advanced,” compelling retailers to invest hundreds of millions annually in cybersecurity measures.

    “All retailers are constantly updating their systems to ensure maximum security,” she added.

    According to technology site BleepingComputer, a ransomware attack believed to have been executed by a hacking group called “Scattered Spider” targeted M&S’s servers.

    The NCSC is collaborating with the affected retailers, while the Metropolitan Police’s Cyber Crime Unit and the National Crime Agency (NCA) are probing the M&S incident.

    “These incidents should serve as a wake-up call for all organizations,” stated NCSC head Richard Horne.

    Labour MP Matt Western, who chairs Parliament’s Joint Committee on the National Security Strategy, expressed that the government needs to take stronger measures to prevent large-scale cyberattacks.

    “As the government wraps up its consultation on strategies to combat ransomware, I hope its response addresses these threats with the seriousness they warrant.”

    —

    Let me know if you need any further adjustments!

  • Ransomware Became Hackers’ Choice in 2024 for Quick Attacks

    Ransomware Became Hackers’ Choice in 2024 for Quick Attacks

    A recent research study has revealed a troubling trend: ransomware attacks are not only increasing in frequency but are also being executed at an unprecedented speed. Experts indicate that malicious actors are launching attacks even quicker than security teams can address them.

    Ransomware-as-a-service is a prevalent method used by cybercriminals, offering a variety of harmful tools and services to customers on a subscription basis. The latest comprehensive analysis from the Barracuda Managed XDR team indicates that the number of ransomware assaults in 2024 surged fourfold compared to the previous year.

    2024 Cyberattacks statistics by Barracuda Managed XDR.
    Barracuda Managed XDR

    In their investigation, researchers analyzed 11 trillion IT events in 2024, identifying 1 million as potentially risky. Among these, 16,812 events were classified as “high-severity threats that required immediate defensive measures.”

    While the availability of Ransomware-as-a-Service offerings may contribute to this upward surge in attacks, the Barracuda Managed XDR team noted that the rapid evolution of ransomware is particularly striking when compared to other forms of cyber threats.

    According to their findings, actors attempting ransomware deployments typically operate undetected for periods ranging from 74 minutes to 2 hours before their activities are uncovered. “This operational model not only broadens the landscape of individuals who can access and execute ransomware but also enhances the complexity and sophistication of the attacks,” the team added.

    Data suggests that while malicious actors can implement malware in just over a minute, the Barracuda Managed XDR can effectively monitor up to 350,000 IT events every second to spot significant threats. Yet despite ongoing advancements in cybersecurity methodologies, hackers are consistently employing more advanced and expedited tactics.

    The security professionals emphasize that organizations can still adopt crucial safety strategies. Implementing multifactor authentication, robust access controls, regular patch management, data protection measures, and conducting cybersecurity awareness training for staff are all effective ways to bolster defenses against these fast-evolving threats.

  • AI Battles Cyber Threats With Its Own Advanced Tools

    AI Battles Cyber Threats With Its Own Advanced Tools

    Hands on a laptop.
    EThamPhoto / Getty Images

    The rapid growth of the generative AI (GenAI) sector has given cybercriminals an advantage in exploiting vulnerable targets. Organizations have become more susceptible to breaches due to this swiftly evolving technology, yet many businesses are increasingly incorporating GenAI into their cybersecurity frameworks.

    A recent Splunk CISO 2024 report sheds light on the current landscape of cybersecurity, highlighting differing perspectives among board members and security professionals on addressing emerging threats. Cybercriminals now have more tools at their disposal, utilizing GenAI in sophisticated ways, such as employing AI chatbots to create malware or crack passwords.

    According to recent findings, GenAI has enhanced existing attacks by 32%, led to a 28% rise in overall attack frequency, and introduced 23% new forms of cyber threats into the ecosystem.

    Moreover, 52% of Chief Information Security Officers (CISOs) expressed an interest in using comparable GenAI technologies to tackle cybersecurity challenges, while only 33% of board members shared this sentiment. Although security professionals seek innovation, many find the pace of evolving requirements challenging, with 41% indicating that demands are increasingly difficult to manage amidst the rising frequency and complexity of cyberattacks.

    In terms of practical applications, 39% of CISOs reported using GenAI tools for risk identification, another 39% for threat intelligence analysis, and 35% for threat detection and prioritization.

    The dual-use nature of GenAI presents a significant challenge, as the perspectives of CISOs and board members often diverge on critical issues that could jeopardize enterprise security. The report found that only 29% of CISOs believed they had sufficient budget support for effective cybersecurity measures, in contrast to 41% of board members who felt their funding was adequate. Overall, 64% of CISOs linked inadequate resources directly to the cyberattacks they’ve had to deal with.

    Currently, AI-driven cyberattacks rank as the top concern for CISOs at 36%, followed by cyber extortion at 24% and data breaches at 23%. As previously noted, hackers swiftly adopted AI tools, such as ChatGPT, to refine their malware creation abilities, drawing attention from governmental agencies like the FBI. Additionally, in the wrong hands, advanced technologies like Generative Adversarial Networks (GANs) can be harnessed to crack passwords with alarming speed.

    Security analysts from TechRadar highlight the importance of maintaining security through robust passwords, multi-factor authentication (MFA), password management solutions, cybersecurity education, and careful assessments of third-party vendor vulnerabilities to safeguard against cyber threats.